HTTP vs HTTPS: How Secure Web Communication Works
Understand the difference between HTTP and HTTPS, how TLS protects web traffic, and what HTTPS can and cannot secure.
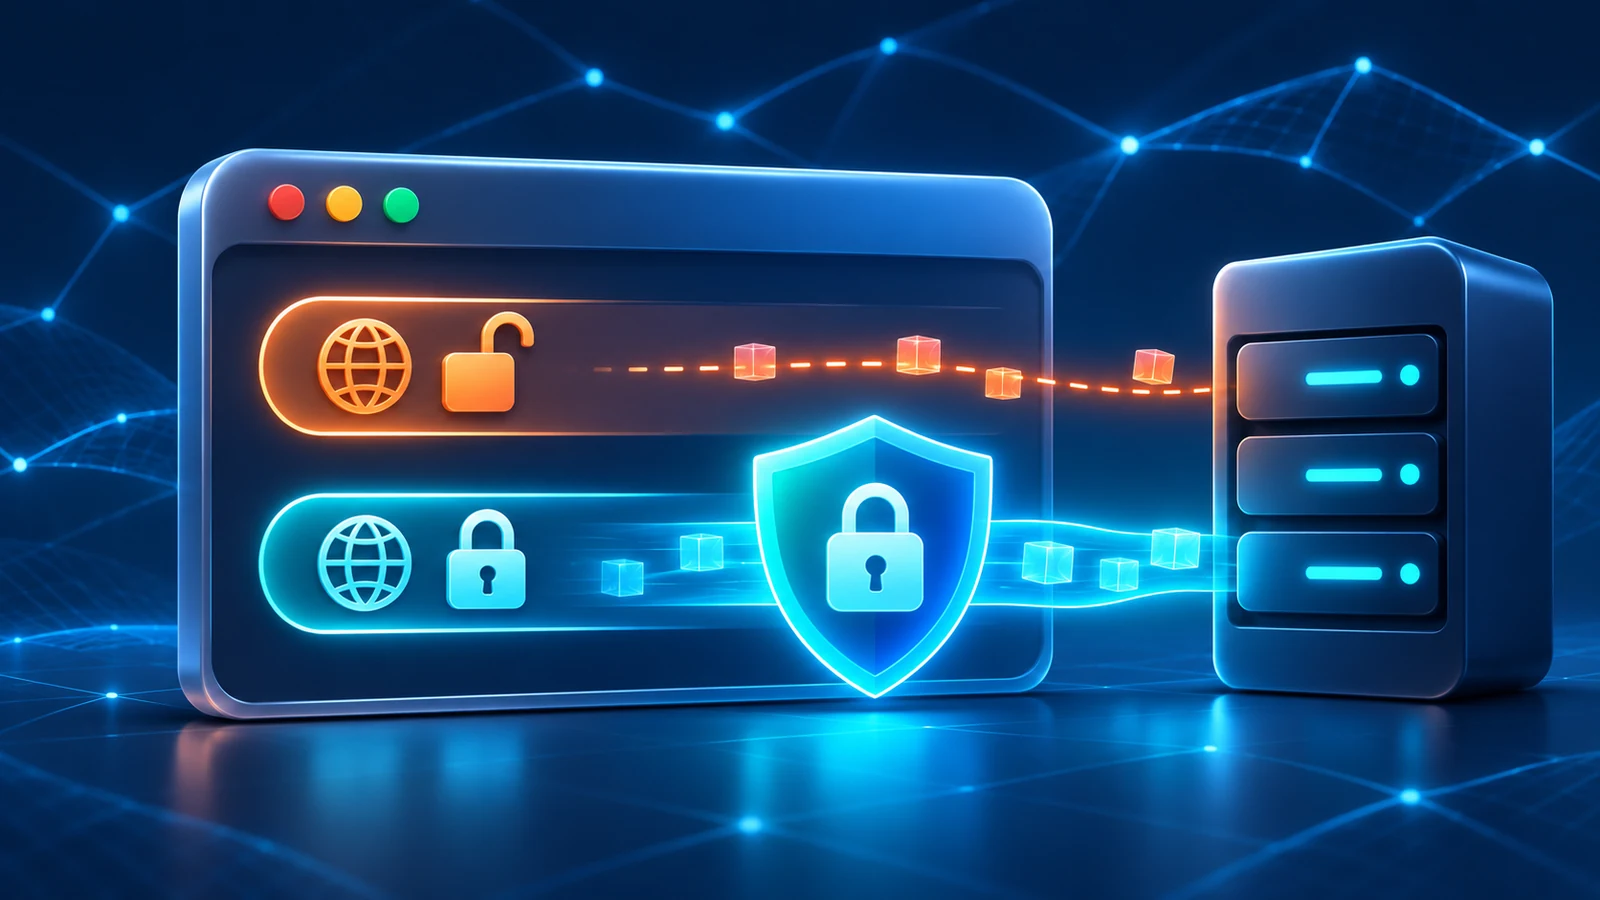
Table of Content
Table of Content
Every time you open a website, your browser and a web server exchange information. That information might be a page you want to read, a search query, a login form, or a payment request. How safely it travels depends in part on whether the connection uses HTTP or HTTPS.
The difference is easy to spot in a web address: HTTPS begins with https://, while HTTP begins with http://. But the extra “S” represents more than a different address format. HTTPS uses Transport Layer Security (TLS) to protect HTTP communication. When configured correctly, TLS helps keep information private in transit, detect tampering, and verify that the browser has connected to a server that can prove its identity for the requested website.
Those protections matter on public Wi-Fi, at home, at work, and anywhere else data passes through networks you do not control. They also matter for ordinary browsing, even when you are not entering a password. This guide explains how HTTP and HTTPS work, what happens when a browser opens a secure page, and where HTTPS’s protection ends.
What Is HTTP?
HTTP stands for Hypertext Transfer Protocol. It defines how a web client usually a browser requests resources from a server and how the server sends responses. Resources can include HTML pages, images, stylesheets, scripts, and other data.
For example, when you open a page, your browser might send a request asking for a particular resource. The server responds with a status code, headers that describe the response, and often the requested content. HTTP is the application-level protocol that gives these messages their structure and meaning. It does not, by itself, encrypt the connection.
In a plain HTTP connection, data travels without TLS protection. A person or system able to observe the connection may be able to read the traffic. Someone who can interfere with the network may also be able to alter or replace unprotected data in transit. This creates risks when users visit websites, submit forms, or receive content over an unsecured connection.
HTTP is still a useful part of web technology, but it lacks the transport security that HTTPS provides.
What Is HTTPS?
HTTPS means HTTP Secure. It uses HTTP over a connection secured with TLS. TLS creates a protected channel between the client and the server; once that channel is established, HTTP messages travel inside it.
The IETF’s HTTP standard describes an HTTPS URI as one that requires secure communication. In the common case, a client connects to the server, establishes TLS, then sends its HTTP request over that secured connection.
HTTPS is not a separate version of HTTP that changes the meaning of web requests. It protects the communication channel used to send them. The page content, request methods, and response codes are still part of HTTP. TLS adds security around the exchange.
The protections provided by TLS are commonly described in three parts:
- Confidentiality: Helps prevent people who can observe the network from reading the contents of the protected traffic.
- Integrity: Helps detect unauthorized changes to data while it is in transit.
- Authentication: Helps the browser check that it is communicating with a server that can prove its identity for the requested domain.
These are transport protections. They do not prove that a website’s content is honest, that a business is legitimate, or that a user’s device is free of malware.
HTTP vs HTTPS: The Main Differences
With HTTP, a browser and server exchange web messages without TLS protection. With HTTPS, TLS protects those messages in transit and provides a way for the browser to verify the server’s identity.
In practice, the difference affects privacy and trust. If a user submits information through an HTTP page, that information may be exposed to parties who can monitor the connection. On HTTPS, the data is encrypted between the browser and the server, making it much harder for an outside observer to read or modify it while it travels.
HTTPS also helps protect the pages and files a browser receives. Without transport encryption and integrity checks, an attacker who can interfere with a connection might inject unwanted content or change a response. With a correctly configured HTTPS connection, unauthorized changes to protected traffic should be detected.
A browser’s padlock or security indicator means that a secure connection was established and that the browser accepted the certificate for the site. It does not mean the site itself is safe to use. A fraudulent or compromised website can still use HTTPS.
How TLS Makes HTTPS Secure
TLS stands for Transport Layer Security. It is a protocol that establishes a secure channel between two endpoints. HTTPS uses TLS to protect HTTP traffic. TLS is designed to provide authentication, confidentiality, and integrity for data sent after the connection has been established.
When a browser starts an HTTPS connection, it and the server perform a process called the TLS handshake. This is a negotiation that helps them agree on how to protect the session and establish the cryptographic keys used to secure later traffic.
A simplified version of the process looks like this:
- The browser contacts the server. It sends information about the TLS versions and cryptographic options it supports, along with other connection details.
- The server responds. It selects compatible options and sends information that lets the browser authenticate it, usually including a digital certificate.
- The browser checks the certificate. It checks, among other things, whether the certificate is trusted for the domain it is visiting and whether it is valid under the browser’s certificate rules.
- The browser and server establish shared keys. They use the negotiated cryptographic process to set up keys for protecting the connection.
- They exchange protected HTTP traffic. Once the handshake succeeds, HTTP requests and responses travel inside the TLS-protected connection.
This is a simplified explanation; exact messages and options depend on the TLS version and connection. In TLS 1.3, the handshake negotiates cryptographic parameters, authenticates the server, and establishes the key material used to protect application traffic.
Why Public-Key Cryptography Matters
TLS uses public-key cryptography as part of authentication and key establishment. A website’s certificate contains its public key and information that helps associate that key with a domain. The corresponding private key is kept by the server and should not be shared.
The browser does not simply accept any certificate a server sends. It checks whether the certificate is valid for the requested website and whether it chains back to a certificate authority the browser trusts. If those checks fail, the browser may show a security warning or refuse to establish the connection.
After authentication and key establishment, TLS uses session keys to protect the traffic. This approach lets the browser and server create a private connection without sending the session’s encryption keys as plain text across the network.
What Is an SSL/TLS Certificate?
People often call HTTPS certificates “SSL certificates,” but current secure web connections use TLS. SSL is the older predecessor to TLS and is no longer considered secure for modern use. The phrase “SSL certificate” remains common, even though “TLS certificate” is more technically accurate.
A certificate helps a browser verify that a server is authorized to represent a domain. It includes a public key and details about the domain or domains it covers. A certificate authority (CA) digitally signs the certificate, and browsers rely on trusted CAs as part of their verification process.
Certificates can be issued for a single domain, multiple named domains, or a wider set of subdomains, depending on the certificate type. A site owner must configure the server to present a certificate that is valid for the address people use to visit the site.
A certificate does not encrypt data by itself. The certificate supports authentication during the TLS handshake; TLS then establishes the protected channel that encrypts traffic and checks its integrity.
What Information Does HTTPS Hide?
HTTPS protects the contents of HTTP messages while they travel between the browser and the server. That includes the body of a request or response and many HTTP headers. For example, TLS helps protect a login form’s submitted password from being read by someone observing the network.
However, HTTPS does not hide everything about a connection. Network observers may still be able to infer that a device is communicating, when it is communicating, how much data it sends, and sometimes which service or network address it is contacting. The precise visibility depends on the network, DNS setup, TLS features, and other technical details.
HTTPS also does not hide information from the website receiving the request. The server must process the data the user sends. If a user shares personal information with a site, that site can still store or use it according to its systems and policies. HTTPS protects data in transit; it is not a substitute for careful data handling by the service.
What HTTPS Does Not Protect Against
HTTPS is essential, but it cannot solve every security problem. Its protections apply to the connection between the browser and the server; they do not guarantee that everything at either end is safe.
HTTPS does not guarantee that:
- A website is honest, reputable, or free from scams.
- A website’s server has not been hacked.
- A user’s computer or phone is free from malware.
- A person is sending information to the right organization if they have opened a lookalike domain.
- A website will store personal data safely after receiving it.
- A weak password or reused password is safe.
- A link or download is harmless.
A phishing website can use HTTPS and still trick visitors into entering their information. The certificate can show that the connection is secured to that domain, without proving that the domain belongs to the brand a visitor had in mind. Always check the domain name carefully, especially before signing in or making a payment.
HTTPS also cannot prevent an attacker from abusing a compromised device or account. If malware records keystrokes before data enters the protected connection, TLS cannot stop that. Similarly, if a website has a security flaw that exposes stored data, transport encryption alone will not fix it.
Why HTTPS Matters on Public Wi-Fi
Public Wi-Fi is one setting where HTTPS’s protection is easy to understand. Other people on the same network, or systems that manage the network, may have opportunities to observe or interfere with traffic that is not encrypted.
On a correctly configured HTTPS connection, TLS helps protect the contents of the exchange from network observers and makes unauthorized changes detectable. This is useful whether you are logging in, checking a private page, or simply reading an article.
HTTPS does not make every public Wi-Fi network trustworthy. A fake network could still direct users to misleading pages, and a user might still enter information on a phishing site. But HTTPS significantly improves the protection of the connection to a site when the browser verifies the site’s certificate successfully.
HTTP and HTTPS in the Browser
When you type a web address, the browser uses its schemehttp or httpsto decide how to access the resource. In the common case, http:// uses port 80 and https:// uses port 443 by default, though servers can use other ports.
Many sites automatically redirect visitors from HTTP to HTTPS. A redirect is a response telling the browser to request a different address. This can make it easier for visitors who type a domain without a scheme, but the initial HTTP request still matters: before the redirect, the browser’s first contact may be unencrypted.
Websites can use HTTP Strict Transport Security (HSTS) to tell browsers to use HTTPS for future visits to that site. Once a browser has received and accepted the HSTS policy, it can avoid making an HTTP request for that domain on later visits, subject to the policy’s settings and browser behavior. HSTS can reduce the chance of a connection being downgraded to HTTP.
A website must also make sure its HTTPS pages do not load important files over HTTP. When a secure page loads some resources using an insecure connection, that is called mixed content. Depending on the type of resource and browser behavior, insecure content may be blocked or may weaken the page’s protection.
How Website Owners Can Use HTTPS Well
For website owners, enabling HTTPS is the starting point. A secure setup also needs proper certificate management, sensible TLS configuration, and consistent use across the site.
A website should use a certificate that covers the domains visitors actually use, renew it before it expires, and keep the server’s TLS configuration maintained. It should redirect HTTP requests to HTTPS and use HSTS when appropriate. Site owners should also update internal links and embedded resources so pages do not rely on HTTP files.
TLS versions and configuration choices matter. Website operators should avoid obsolete protocols and weak settings, and should keep their hosting software and security configuration up to date. The OWASP Transport Layer Security Cheat Sheet provides implementation guidance for application teams using TLS.
HTTPS should cover all pages, not only login or payment screens. A page that appears harmless can still reveal a user’s browsing activity or load scripts that affect the rest of the site. Protecting the entire site gives visitors a more consistent security baseline.
Does HTTPS Help with SEO?
HTTPS is a positive signal for a website’s overall quality and user experience, and it is widely expected for modern websites. It can also prevent browser warnings that may discourage visitors from continuing to a site. That makes it a sensible part of maintaining a trustworthy website.
However, HTTPS alone does not guarantee high search rankings or indexing. Search engines consider many factors, and a secure connection cannot compensate for thin, duplicated, misleading, or technically inaccessible content. HTTPS is best understood as a baseline for a modern site rather than a shortcut to ranking well.
Website owners moving from HTTP to HTTPS should update canonical URLs, internal links, XML sitemaps, and analytics or other integrations where needed. They should also set up redirects carefully so both visitors and search crawlers reach the intended secure pages.
How to Check Whether a Website Uses HTTPS
Start by looking at the address bar. A secure page should use https:// in its address. Browsers may display a padlock or another site information icon, though the design varies between browsers and can change over time.
You can also inspect the address itself. A misspelled or unfamiliar domain can still have HTTPS, so check that the domain is the one you intended to visit. If the browser displays a certificate or connection warning, do not ignore it just to continue especially if you are about to enter personal or payment information.
For a website you operate, check that:
- All key pages load over HTTPS.
- HTTP addresses redirect to the correct HTTPS pages.
- The certificate is valid for every domain visitors use.
- The site does not load important scripts or resources over HTTP.
- The certificate renews reliably before it expires.
- The TLS configuration follows current security guidance.
These checks help distinguish “the site has a certificate” from “the site consistently uses HTTPS correctly.”
Frequently Asked Questions
Is HTTPS completely secure?
No connection can make every part of web use completely secure. HTTPS helps protect traffic between the browser and the server, but it does not prove a site is legitimate or protect against every problem on the user’s device or the website itself.
Can someone read my password over HTTPS?
A correctly established HTTPS connection encrypts the traffic while it travels between your browser and the server, making it much harder for a network observer to read the password in transit. The website still receives the password, so use a trusted site and a unique, strong password.
What does the padlock icon mean?
It generally indicates that the browser established a secure connection and accepted the site’s certificate. It does not mean the website is trustworthy, ethical, or free from malicious content. Check the domain before sharing sensitive information.
Is HTTP still used?
Yes. Some sites or resources may still use HTTP, but it does not provide the transport protection that HTTPS does. Modern website owners should use HTTPS consistently.
What is the difference between SSL and TLS?
SSL is the older protocol family that came before TLS. Modern HTTPS uses TLS. “SSL certificate” is still a common phrase for the certificate used to support HTTPS, even though TLS is the current protocol name.
Does HTTPS protect my privacy from the website?
No. HTTPS protects traffic in transit between your browser and the server. The website still receives and processes the information you send, so its privacy practices and security controls matter too.
Conclusion
HTTP defines how browsers and servers exchange web requests and responses. HTTPS uses TLS to protect that exchange with encryption, integrity checks, and server authentication. During the TLS handshake, the browser and server negotiate the connection, validate the site’s certificate, and establish keys for protecting later traffic.
Those protections make HTTPS important for everyday browsing, not just logins and payments. But HTTPS is one layer of web security. It protects the connection; it does not guarantee that a site is honest, that a device is safe, or that a website will handle data responsibly. Check the address, use trusted sites, and treat HTTPS as a necessary foundation for safer web communication.